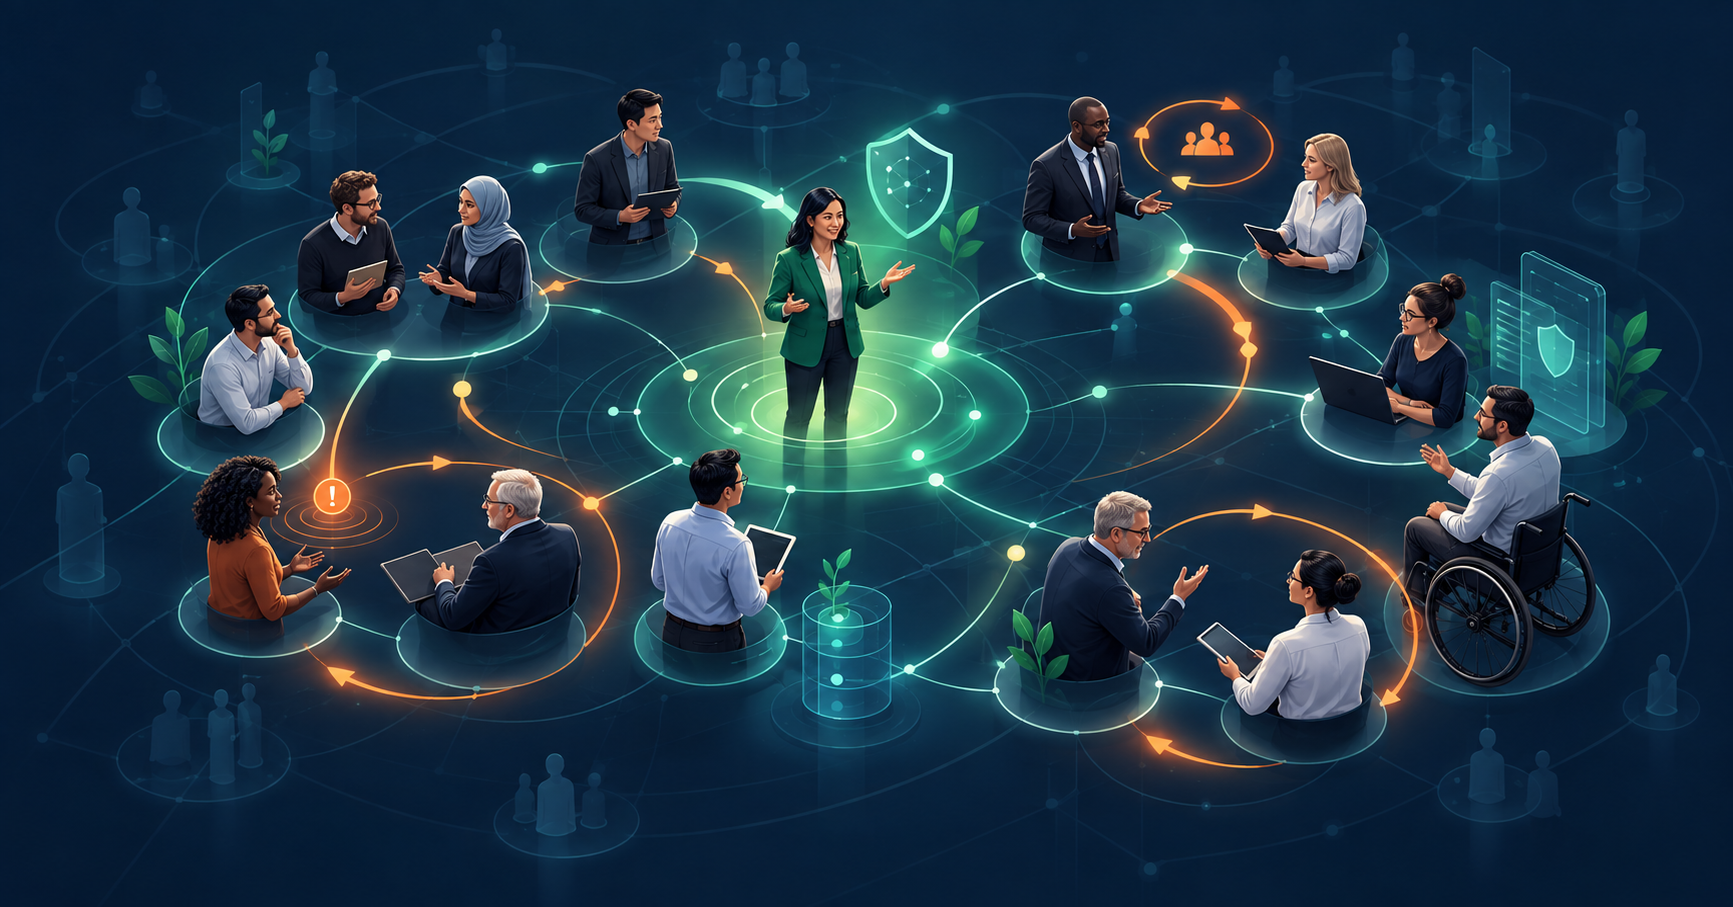
Most organisations treat security behaviour as a plumbing problem. There is a pipe. Training goes in one end; compliant behaviour comes out the other. If the output is disappointing, you increase the pressure: more modules, more phishing simulations, more posters in the lift. The model is linear, and it is wrong.
An organisation is a complex adaptive system. Once you accept that, much of what feels mysterious about security culture becomes explicable, and a different set of interventions becomes available.
What complex actually means
Complexity is not the same as complicated. A jet engine is complicated. It has thousands of parts, but each part does one predictable thing, and if you understand the parts you understand the whole. An organisation of eight thousand people is complex. The behaviour of the whole cannot be deduced from the behaviour of the parts, because the parts keep changing each other.
Three properties matter most for anyone trying to shift security behaviour.
Emergence. Culture isn't something anyone decides. It comes from thousands of small, local interactions: a manager who sighs when someone raises a concern, a team that quietly shares a password because the approvals process takes four days, a senior leader who forwards an unverified attachment and nobody says anything. None of these people set out to create a culture. The culture emerged anyway.
Feedback loops. Behaviour in a system feeds back on itself. A team that reports incidents promptly gets faster support, which makes reporting feel worthwhile, which produces more reporting. A team that gets blamed for the first incident it reports stops reporting, which means problems fester, which means the eventual incident is worse, which confirms to leadership that this team cannot be trusted. Both loops are self-sustaining. Neither was designed.
Non-linearity. In a linear system, twice the input gives twice the output. In a complex system, the relationship between effort and effect is uneven. You can double a training budget and see nothing. You can move one well-connected person into a different team and watch an entire department's reporting behaviour change within a quarter. The lever that matters is rarely the most expensive.
Why linear interventions fail
The standard awareness programme assumes that behaviour is a function of knowledge. Tell people the right thing, and they will do the right thing. Two decades of behavioural science say otherwise, and anyone who has ever known they should go to the gym already understands the gap between knowing and doing.
The COM-B model, which underpins how we think about measurement at CyBehave, breaks behaviour into three components: capability, opportunity and motivation. Training addresses capability and only capability. It does almost nothing for opportunity, which is about whether the environment makes the behaviour possible and easy, and it often actively damages motivation, because mandatory annual modules are one of the most reliable ways to teach people that security is a box to be ticked rather than a thing that matters.
But the deeper problem is that even a programme that addressed all three components for each individual would still miss the point. In a complex system, individuals are not the unit of change. Relationships are.
Consider phishing. The person who clicks is the visible failure. But whether they click depends on whether the last person who reported a suspicious email in their team was thanked or ignored. It depends on whether the team's workload leaves any room for the three seconds of doubt that reporting requires. It depends on whether the person sitting next to them would notice, and whether noticing would be welcome. The click ends a chain of social conditions, and training the clicker does nothing about the chain.
Working with the system rather than against it
If you accept the complexity framing, four practical shifts follow.
- Stop optimising the average. Find the nodes.
In any organisation, influence is not evenly distributed. A small number of people are disproportionately connected: they are the ones colleagues go to with questions, the ones whose habits get copied, the ones who set the tone in a team without holding any formal authority. Organisational network analysis can identify them. Once you know who they are, the intervention changes entirely. You are no longer trying to reach eight thousand people through a broadcast. You are trying to reach three hundred people through relationships, and letting the network do the rest.
This is the whole logic behind a Security Champions Network done properly. The champions are not a distribution list for security messages. They are the nodes through which behaviour propagates.
2. Design for feedback, not for delivery.
A well-designed intervention creates a self-sustaining loop. A poorly designed one requires constant energy from the security team to keep going, and stops the moment attention moves elsewhere.
The practical test is simple. Ask what happens to the behaviour if the security team disappeared for six months. If the answer is that it would collapse, you have built a delivery mechanism, not a behaviour change. If the answer is that it would carry on because reporting gets people help, because champions have their own reasons to keep going, because managers have started asking about it in team meetings, then you have changed the system.
3. Expect delay, and measure for it.
Complex systems respond slowly and then suddenly. Interventions that look like failures at three months can be the beginning of something at nine. This is genuinely difficult to manage, because most governance cycles want quarterly evidence and most sponsors want a graph that goes up.
The answer is to measure leading indicators separately from outcomes. Network strength, which is a structural property of how well connected your champions and influencers are, moves before behaviour does. Programme capability, meaning whether the machinery is in place to sustain the effort, moves before network strength. If you only measure the behavioural outcome, you will kill programmes just before they start working. This is why the Heroes measurement model separates these three sources rather than blending them into a single score that hides where the movement actually is.
4. Accept that you cannot control it. You can only shape the conditions.
This is the hardest shift, especially for security leaders trained to think in terms of controls. You cannot mandate culture. You cannot enforce trust. What you can do is change the environment so the behaviours you want become easier, more socially rewarded, and more visible than the behaviours you don't want, and then let the system find its way.
That means removing friction from the right path before adding friction to the wrong one. It means making sure the first reporting experience is a good one. It means treating a champion who leaves as a signal about the conditions, not a recruitment problem. It means noticing which feedback loops you are currently reinforcing, because you are always reinforcing some, whether you intended to or not.
The measurement problem
Most of what gets sold as risk measurement is telemetry: click rates, completion rates, the number of people who used a password manager this month. These are system outputs, and they are useful as far as they go. But telemetry cannot tell you why the number is what it is, and it cannot tell you what it will be next quarter, because it does not measure any of the conditions that produce it.
Measuring a complex system means measuring structure and disposition, not just activity. Who is connected to whom. Whether people believe reporting is safe. Whether the champions network is actually a network or a mailing list with a logo. These are psychometric and structural questions, and they require instruments designed for the purpose, not data scraped from a phishing platform.
This is not a comfortable message for anyone who has already invested in a dashboard. But if the underlying model is wrong, a better dashboard just gives you a more precise view of the wrong thing.
What this looks like in practice
The organisations I have seen make real progress share a pattern. They stopped trying to change everyone and started changing the conditions. They invested in finding and supporting the people who already had influence rather than manufacturing influence through job titles. They measured the network, not just the outcomes. They gave interventions time, and they built the case for that time using leading indicators rather than promises.
None of this is quick, and none of it produces a tidy graph in the first quarter. But it works because it aligns with how organisations actually behave, not how a training vendor would like them to.
Security behaviour is an emergent property of a complex system. The sooner we design our programmes as if that were true, the sooner they will start delivering something other than completion rates.