A technologist who went looking for why people behave insecurely

I run CyBehave, research Security Champions networks at the University of Hertfordshire, and write about the human side of cyber risk. This page is the short version of who I am, and a running record of what I have published.

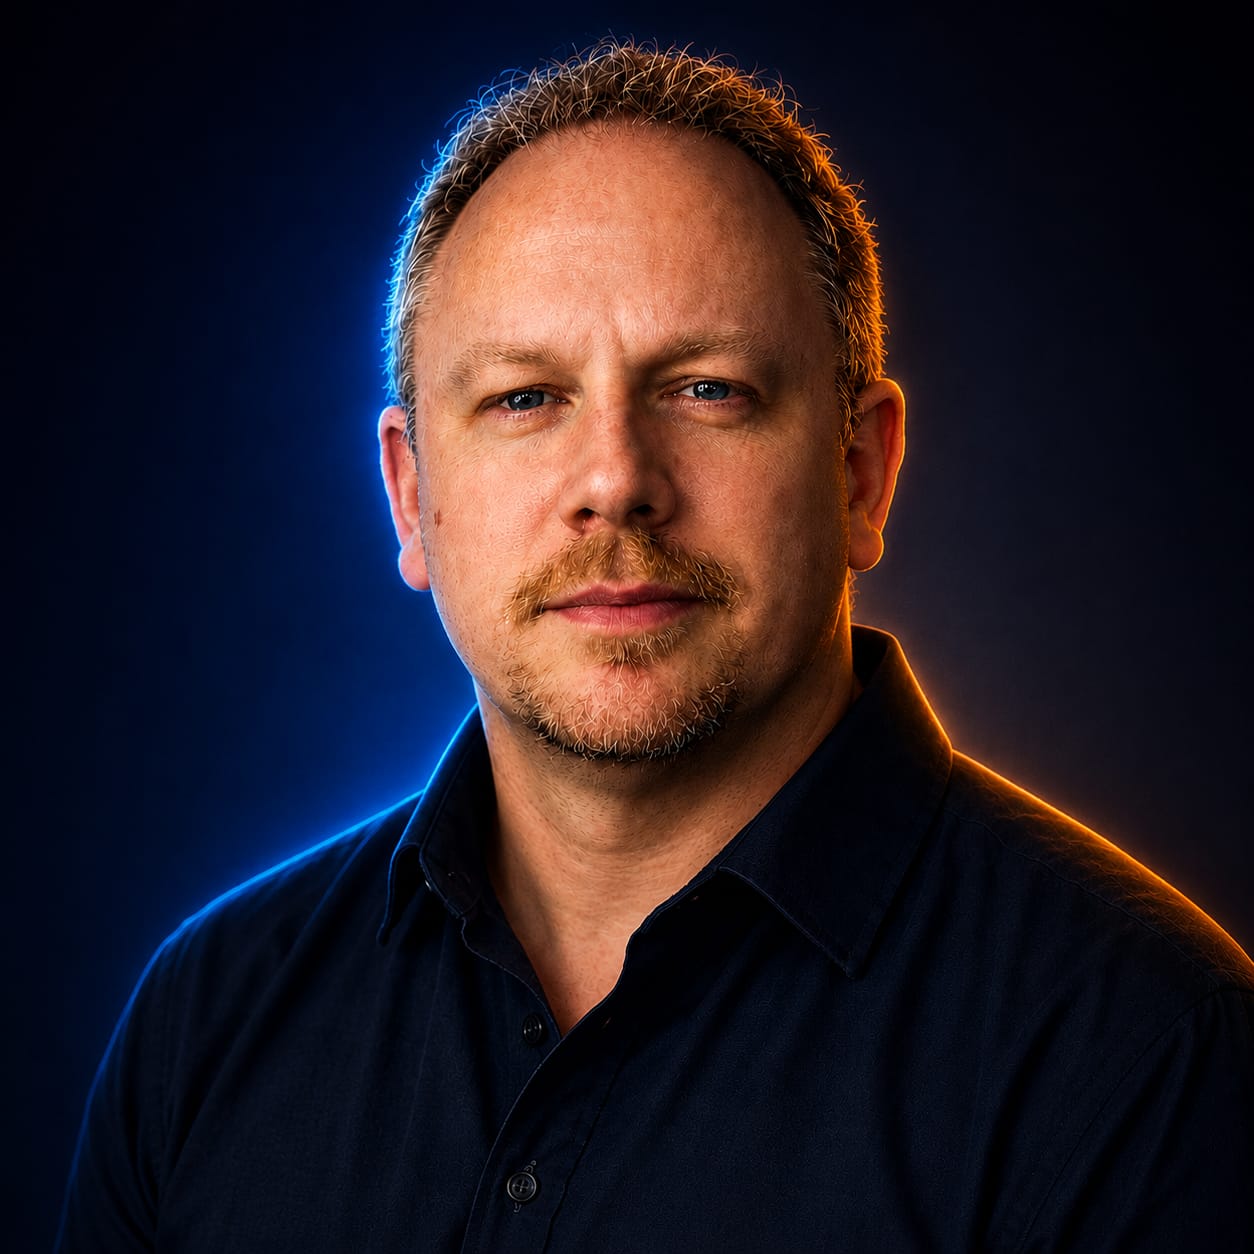
Portrait of Andy Wood

Still excited by technology. Careful about what I ask it to do.

Technology has been part of my life since I was young, and I have never lost the excitement of seeing what it can do. My career followed that instinct: infrastructure engineering first, then security architecture, then leading security for a large enterprise. Spend long enough on the defending side, though, and you see the same thing over and over. The technology usually does what it was built to do. What decides the outcome is a person in a hurry, a message that looked right, or a secure route so awkward that someone found a way round it.

Security careers are mostly built through technology or through process, and neither teaches you much about why people do what they do. So I went looking elsewhere, in behavioural science, cyber psychology and cultural anthropology, and I have spent the years since turning what I found into something a practitioner can pick up on a Monday morning and use. That is what CyBehave is for. Small changes in behaviour add up, and given time they become a culture that people take home with them at the end of the day.

My work runs on two tracks that feed each other. CyBehave is where the thinking happens: the research at the front of the field, the guidance practitioners actually use, a point of view on where the industry should be heading, and HEROES by CyBehave, the platform that turns the research into a working product. Capita is where that thinking meets a large, complex business. There I lead security strategy and culture across the group, and my job is to put the CyBehave research to work: to make security something the workforce carries with them rather than something done to them, and to move security decisions left, to the people deciding what the business does and the people doing it. Each side keeps the other honest. The research tells Capita what to try, and Capita tells the research what survives contact with a real organisation.

Alongside both I am a doctoral researcher at the University of Hertfordshire. I have built and led Security Champions networks of various sizes, in organisations from private enterprises through to public sector departments, and my research maps how influence travels through those networks and where it gets stuck. Security culture can be measured once you know what to look at.

More recently the same questions have followed me into AI. Agents that act on their own behalf pick up habits, copy each other and drift, and governing that is a behavioural problem as much as a technical one. My latest papers are about exactly that, and the newest pair asks whether what we know about human social influence holds in populations of AI agents, then puts it to the test. I hold one firm view through all of it: technology should enable people, not stand in for them.
At a glance

Andy Wood MBA  MSc  CSci  CITP  FBCS

Founder, CyBehave

  • Doctorate in Behavioural Cybersecurity (in progress), University of Hertfordshire
  • MBA in Business and Cybersecurity Management, Coventry University
  • MSc in Computer Security, De Montfort University
  • Chartered Security Architect (SABSA)
  • Chartered IT Professional (CITP)
  • Chartered Scientist (Behavioural Cybersecurity) (CSci)
  • Fellow of the BCS

Find me elsewhere

What I have written, newest first

Five books, a journal article and a growing set of preprints. The books were written for practitioners. The papers are where I test the ideas properly, and the preprints are free to read.

In progress
Research Ongoing · University of Hertfordshire

Doctoral research: Security Champions Networks and organisational network analysis

My doctorate maps how security influence moves through a champions network, who it reaches, and where it stalls. The aim is to give programme leads something better than headcount to judge a network by.

2026
Preprint Oct 2026 · SSRN preprint

Behavioural Convergence Theory: Independent Evidence from Multi-Agent Systems Research, and What Its First Tests Found

Between 2024 and 2026, researchers running populations of language-model agents kept finding behaviour that looked like social psychology: conformity to peers, deference to claimed expertise, conventions forming from nothing. None of them set out to test that. This paper reads their results through the four-layer, sixteen-factor model of human cyber risk I use with people, rates how well each human-to-agent analogy holds up against that independent evidence, and finds it strongest at the social layer, the one the original framework was most cautious about.

Preprint Oct 2026 · SSRN preprint

Same Behaviour, Different Rules: Pre-Specified Tests of Human Social-Influence Regularities in Language-Model Agent Populations

The companion paper puts the theory to the test: four predictions, with every pass and fail criterion fixed before a single result came in, run on populations of four open-weight models across roughly 720,000 logged model calls. One prediction held and three did not. The regularities are real and the human instruments measure them, but the models that carry a norm do so by different individual rules, so an intervention designed for people cannot be assumed to work on an agent until the mechanism has been measured on that model.

Preprint Oct 2026 · SSRN preprint

The Normative Repository: Grounding Agentic AI in Organisational Norms, with Norm Attestation as a Compromise Signal

People pick up security culture through repetition and the example of colleagues. AI agents pick up none of it, but they will read a file and act on it. This paper proposes a signed, version-controlled repository of organisational norms that agents load and re-check on a fixed schedule, and argues that a missed or stale check is a useful sign an agent has been hijacked or has drifted.

Preprint Oct 2026 · SSRN preprint

Brace: A Third Class of Behavioural Intervention for Adversarial Choice Architecture in Cybersecurity

Nudge and boost both assume that whoever designed the decision is on your side. In security, the person who designed it is often the attacker. Brace is my answer to that gap: a response a team agrees and rehearses in advance, so that when the pressure arrives there is no decision left to manipulate.

Book 2026

SINGULARITY: Choosing Humanity's Future in the AI Age

A step outside security and into the wider question of where AI is taking us. It follows the technology from the tools already saving lives to the systems already deceiving people, and asks what choices are still ours to make.

2025
Book 2025

The Rise of the Security Champion: From Awareness to Action

The book I started first and finished later. A practical guide to finding, recruiting and keeping Security Champions, written from the experience of building networks in organisations of very different sizes.

Book 2025

DECEIVED: Why We Click, Trust, and Get Hacked

Fraud is far older than the internet. This one traces the same tricks from counterfeiters and confidence men through to phishing and deepfakes, and explains why trust, habit, fear and urgency still work on all of us.

Book Apr 2025

Behaviour Change Playbook for Cyber Security

The how-to companion to the culture book. It takes the Behaviour Change Wheel and COM-B and walks through using them on real security behaviours, one step at a time, with case studies.

2024
Book Oct 2024

Building a Cyber Security Culture: A Strategic Guide to Protecting Your Business

My first book. It makes the case that security is a people question before it is a technology one, and sets out how an organisation gets from annual awareness training to a culture where secure behaviour is simply how work is done.

2017
Journal article 2017 · International Journal of Critical Infrastructures

A security architectural pattern for risk management of industry control systems within critical national infrastructure

A peer-reviewed journal article from my security architecture years, written with Ying He, Leandros A. Maglaras and Helge Janicke and published in the International Journal of Critical Infrastructures. It sets out an architectural pattern for managing risk in the industrial control systems that sit underneath critical national infrastructure.

The full, maintained record is on my ORCID profile: https://orcid.org/0009-0006-0069-1835

See where the research goes

The frameworks are published openly, and Heroes puts them to work in a Security Champions programme.